A team of 5 to 50 people needs three named roles to govern AI: an AI governance lead who owns the policy, the AI tool register and the quarterly review; a tool owner for each AI tool in use; and an incident first responder who takes the first call when something goes wrong. One person can hold two of these in a team of ten. What matters is a name next to each role. NIST's AI Risk Management Framework puts it as "Roles and responsibilities and lines of communication related to mapping, measuring, and managing AI risks are documented and are clear to individuals and teams throughout the organization" (NIST AI 100-1, GOVERN 2.1).
The legal side is narrow. The EU AI Act asks deployers of high-risk systems to assign human oversight to "natural persons who have the necessary competence, training and authority, as well as the necessary support" (Article 26(2), consolidated text of 27 July 2026). It does not require a governance committee, a chief AI officer or any of the role titles below. Those are our recommendation for keeping AI use accountable in a small company.
The three roles and who usually holds them
| Role | Who usually holds it | Owns | Does not need to |
|---|---|---|---|
| AI governance lead | COO, head of operations, a founder, or a senior manager with compliance scope | AI policy, the tool register, approving new tools, the quarterly review, the incident response process, reporting to leadership | Review every AI output or have a technical AI background |
| Tool owner (one per tool) | The person who pushed for the tool, often a department lead | Use within policy, briefing their team on the tool's rules, reporting incidents, confirming at review that the tool is still needed | Approve the tool alone |
| Incident first responder | One named person, with a named backup | Taking the first report, preserving evidence, starting the escalation path below | Decide on regulator notification (that is the lead with legal) |
Everyone else follows the AI acceptable use policy, keeps restricted data (personal data, credentials, confidential IP) out of unapproved tools, and reports incidents to their manager or the lead.
Our strongest opinion on this page: assign the tool owner before the tool goes live. If nobody wants to own a tool, treat that as a reason to reject it. The tool register the lead keeps is the inventory NIST asks for in GOVERN 1.6: "Mechanisms are in place to inventory AI systems and are resourced according to organizational risk priorities."
RACI for the core activities
| Activity | AI governance lead | Tool owner | Department manager | All staff | Leadership |
|---|---|---|---|---|---|
| Write and update AI policy | R/A | C | C | I | I |
| Maintain AI tool register | R/A | C | I | I | I |
| Approve new AI tools | A | R | C | I | I |
| Brief team on tool rules | I | R/A | C | I | I |
| Investigate incidents | R/A | R | C | I | I |
| Quarterly governance review | R/A | R | C | I | I |
| Report to leadership | R/A | I | I | I | I |
| Escalate compliance issues | R/A | R | R | I | I |
R = Responsible, A = Accountable, C = Consulted, I = Informed
For a copy-paste version with 12 activities, including vendor DPAs and EU AI Act tasks, use the AI governance RACI template for small teams.
Escalation matrix: who to call for what
Write the escalation path down before the first incident. The only fixed clock in this table comes from the GDPR: a controller notifies a personal data breach to the supervisory authority "without undue delay and, where feasible, not later than 72 hours after having become aware of it" (GDPR Article 33(1)).
| Scenario | First contact | Second contact | Escalates to |
|---|---|---|---|
| Personal data breach involving an AI tool | Incident first responder | AI governance lead + legal/DPO | Supervisory authority (GDPR Art. 33: 72 hours where feasible) |
| Biased AI output affecting a customer decision | Tool owner | AI governance lead | Legal |
| Unapproved AI tool found in use | Manager | AI governance lead | None unless restricted data went in |
| Vendor changes its AI training or data policy | AI governance lead | Legal | Tool owners (update the register) |
| AI-assisted HR decision challenged by an employee | HR lead | Legal | AI governance lead |
| Regulator asks about your AI use | Legal | AI governance lead | Leadership |
| AI system failure affecting customers | Tool owner | Engineering | AI governance lead |
Keep this matrix inside your AI incident response plan, where the person on call will look for it.

Image: Unsplash, used under the Unsplash License.
Assigning the roles in a week
Start by naming the AI governance lead, even before a policy exists. A one-line message to the team does it: "From today, [Name] owns our AI governance. Ask them about AI tools and incidents."
Then go through your AI tool register and put a tool owner next to every approved tool. A tool with no owner goes on the agenda for the next review.
Write the names into your AI policy, together with how to request a new tool and how to report an incident. Names, not only job titles, because titles change hands without anyone updating the policy.
Last, add two sentences to onboarding: who owns AI governance, and where to report a concern. That is the smallest version of NIST GOVERN 2.2, under which personnel "receive AI risk management training to enable them to perform their duties"; teams using Annex III systems will need more than two sentences.
EU AI Act: what Article 26 asks of deployers
Article 26 applies to deployers of high-risk AI systems. For the systems listed in Annex III, the high-risk rules apply from "2 December 2027" under the consolidated text as amended by Regulation (EU) 2026/1744. Annex III covers areas including biometrics, critical infrastructure, "Education and vocational training", employment and workers' management, and credit scoring ("evaluate the creditworthiness of natural persons").
| Article 26 paragraph | What it requires | Who holds it in our structure |
|---|---|---|
| 26(1) | Technical and organisational measures to use the system "in accordance with the instructions for use" | Tool owner |
| 26(2) | Human oversight assigned to natural persons with "the necessary competence, training and authority" | Tool owner or a named operator, appointed by the lead |
| 26(5) | Monitor the system's operation; tell the provider and market surveillance authority about risks and serious incidents | Tool owner, escalating to the lead |
| 26(6) | Keep the logs the system generates, where under your control, for "at least six months" | Tool owner |
| 26(7) | Employers inform workers' representatives and affected workers before using the system at the workplace | AI governance lead with HR |
| 26(9) | Use the provider's Article 13 information for a GDPR Article 35 DPIA, where applicable | AI governance lead with the DPO |
| 26(11) | Inform people that they are subject to an Annex III system that makes or assists decisions about them | AI governance lead |
If you only use general-purpose tools such as ChatGPT, Claude or Gemini for drafting and research, Article 26 does not apply to that use. Article 4 (AI literacy) is the obligation that does; our EU AI Act guide for small teams covers it.
NIST AI RMF: subcategories that name roles
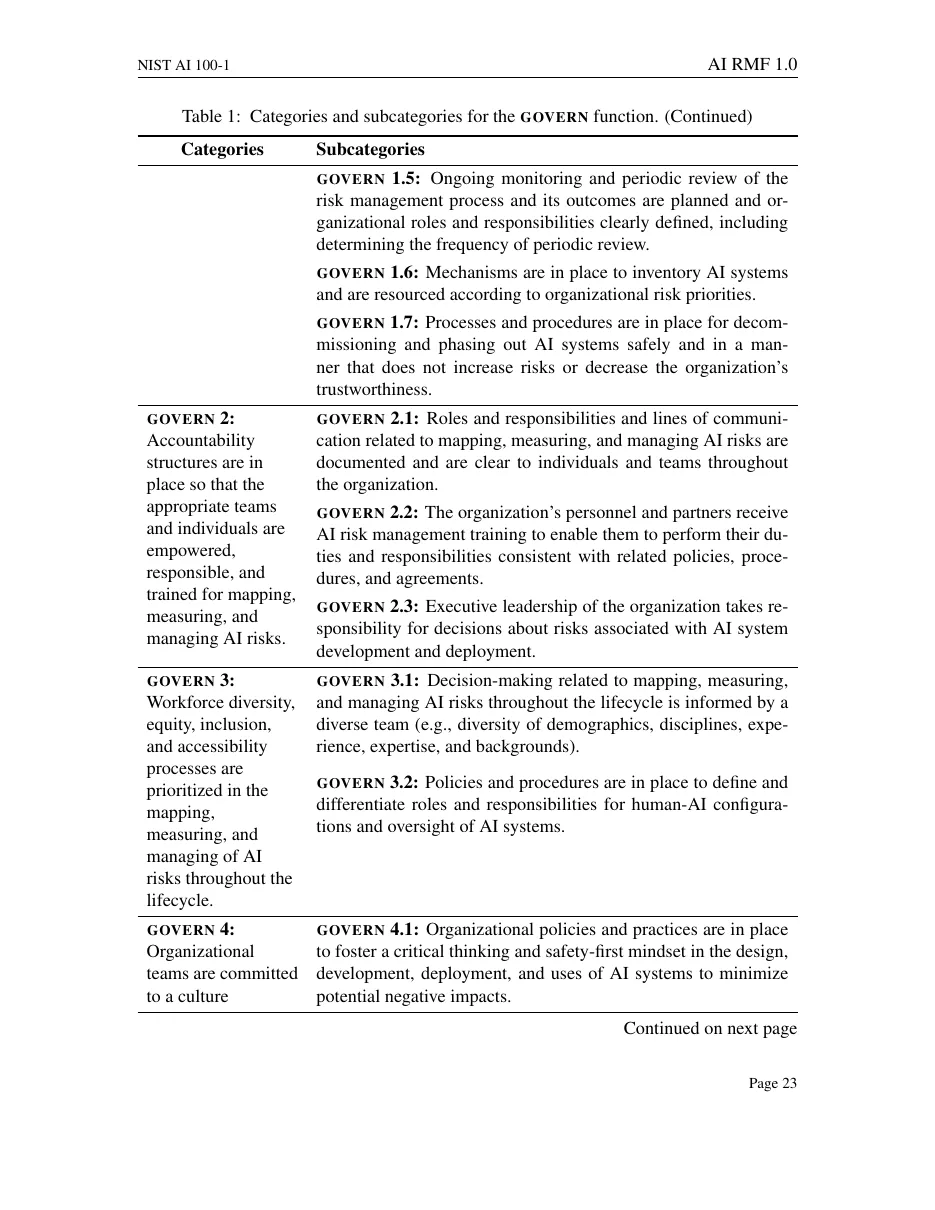
Screenshot: NIST AI 100-1 (AI RMF 1.0), page 23, captured October 29, 2026.
The AI RMF is voluntary. Of its subcategories, these speak directly to who does what. The quoted text is NIST's; the right-hand column is our mapping.
| Subcategory | NIST text (shortened) | Role in this structure |
|---|---|---|
| GOVERN 1.5 | "Ongoing monitoring and periodic review of the risk management process and its outcomes are planned and organizational roles and responsibilities clearly defined" | AI governance lead (quarterly review) |
| GOVERN 1.6 | "Mechanisms are in place to inventory AI systems" | AI governance lead (tool register) |
| GOVERN 2.1 | "Roles and responsibilities and lines of communication … are documented and are clear" | This RACI and escalation matrix |
| GOVERN 2.2 | Personnel and partners "receive AI risk management training" | AI governance lead (onboarding) |
| GOVERN 2.3 | "Executive leadership of the organization takes responsibility for decisions about risks" | Leadership |
| GOVERN 3.2 | Policies "define and differentiate roles and responsibilities for human-AI configurations and oversight" | Tool owner |
| MANAGE 2.4 | Responsibilities "are assigned and understood, to supersede, disengage, or deactivate AI systems" | Tool owner, with the lead's sign-off |
| MANAGE 4.3 | "Incidents and errors are communicated to relevant AI actors" | Incident first responder |
ISO/IEC 42001: certifying the management system
ISO/IEC 42001 is a management system standard, first edition published in December 2023. ISO describes it as one that "specifies requirements for establishing, implementing, maintaining, and continually improving an Artificial Intelligence Management System (AIMS) within organizations" (ISO). The clause text is sold by ISO and we have not quoted it here. If you are heading for certification, your auditor will test the role assignments against the standard itself; the RACI above is a reasonable starting document, not a substitute for reading it.
The certification goes to the organization. For the people involved, the AI governance certification comparison sets out what the individual credentials cost.
When the part-time model stops working
We have no data on the headcount at which a part-time lead stops coping, and we have not found any that we trust. These are the signals we would watch:
- More than one incident a quarter that needs a formal investigation.
- A tool register longer than the lead can walk through in the quarterly review.
- A pending Annex III deployment, where Article 26(2) asks for oversight by people with the competence and authority to do it.
- Customers asking for evidence of AI governance in procurement, rather than a link to the policy.
When two of these hold, budget a fixed share of someone's week for the lead role, or hire. Before a dedicated hire, we would try a small committee of the lead, legal and the engineering lead.
Common mistakes in role setups
Defaulting AI governance to IT puts the policy with the team that controls access, but approving tools for marketing, HR or sales is a business decision. Give IT the access controls and keep tool approval with the lead.
A five-person approval committee for every new tool slows approvals to the point where people stop asking. One decision-maker with a short request form is faster.
"Everyone is responsible for AI governance" leaves nobody to call. Write the names down and update them when people leave.
For background on how larger organizations split these responsibilities, the Brookings Institution published a panel titled "Operationalizing responsible AI":
Correction (October 29, 2026): Earlier versions cited Article 20 for deployer log retention (it is Article 26(6); Article 20 covers providers' corrective actions), Article 26(6) for assigning monitoring to a competent person (oversight is Article 26(2), monitoring Article 26(5)), Article 26(3) for the DPIA (it is Article 26(9)), and Article 26(7) for informing affected individuals (26(7) covers workers and their representatives; individuals are Article 26(11)). They said the three-role structure is the legal minimum for Annex III use; the Act requires competent people for human oversight, not these roles. The NIST AI RMF table misdescribed GOVERN 1.1, 1.4, 2.2, 4.1, 6.1, MAP 5.1 and MANAGE 4.1 and has been replaced with NIST's wording. We removed ISO/IEC 42001 clause claims we could not check against the standard, unsourced time estimates and salary ranges, and a link label that tied an AI register to Article 70 (which designates national competent authorities).
References
- National Institute of Standards and Technology, Artificial Intelligence Risk Management Framework (AI RMF 1.0), NIST AI 100-1, January 2023
- Regulation (EU) 2024/1689 (AI Act), consolidated text of 27 July 2026 on EUR-Lex
- Regulation (EU) 2016/679 (GDPR), EUR-Lex
- ISO, ISO/IEC 42001:2023, Information technology: Artificial intelligence: Management system
- Brookings Institution, Operationalizing responsible AI (video)
Related Reading
- Microsoft Cut 4,800 Jobs and Called It an AI Story
- AI governance guide for small teams
- AI incident response plan template
- EU AI Act compliance guide for small teams
- AI governance metrics dashboard
- AI governance RACI template for small teams
- AI governance certification comparison: AIGP, ISO 42001 lead auditor, AAIA
- AI regulation deadline calendar 2026, every jurisdiction
- AI risk decisioning governance checklist, for teams where the AI Governance Lead owns decisions that affect automated scoring or credit
- VC AI governance due diligence checklist, what investors ask founders about governance maturity
- AI regulatory readiness scorecard, 25-question self-assessment to benchmark your governance function
- GDPR-compliant AI assistants comparison, side-by-side scoring useful when the AI Governance Lead is reviewing vendor approvals
- Free AI register template, 12-field spreadsheet the AI governance lead maintains
- AI adoption metrics that don't create perverse incentives
- AI governance nonprofits 2026
- AI compliance program maturity model 2026
- AI compliance cost for small teams 2026: what you actually pay
- AI Models 2x More Likely to Refuse Criticizing Repressive Regimes
- OpenAI API governance and data privacy for developers 2026
- UK AI regulation 2026: post-Brexit, what actually applies to your business
- Anthropic AI tax proposal and Sanders sovereign wealth fund bill: enterprise governance implications
- AI incident response plan: what regulators expect when your AI system fails
- FCA AI guidance: good practice checklist for smaller firms