Copy this policy and fill in five fields.
The five fields to replace are marked with [BRACKETS]:
[COMPANY NAME][EFFECTIVE DATE][POLICY OWNER NAME AND TITLE][APPROVED TOOLS], your specific approved AI tools[INDUSTRY-SPECIFIC PROHIBITIONS], uses prohibited in your sector
TL;DR: Copy the template, fill in five fields, and keep the approved tools list as a separate page you can update. The sections map to real rules: GDPR processor contracts, HIPAA business associate assurances, the FTC's ban on fake reviews, and the EU AI Act's AI literacy and transparency articles. Brief staff once; that briefing is also an AI literacy measure.
The Policy Template
[COMPANY NAME] AI Acceptable Use Policy
Version: initial issue
Effective: [EFFECTIVE DATE]
Owner: [POLICY OWNER NAME AND TITLE]
Review cycle: Annual (or when a significant new AI tool is deployed)
Purpose
This policy defines how employees at [COMPANY NAME] may use AI tools and automated systems in their work. It protects the company, our customers, and our data while enabling the productivity benefits of AI.
This policy applies to all employees, contractors, and third parties who access [COMPANY NAME] systems or handle company data.
Section 1: Approved AI Tools
The following AI tools are approved for business use. All other AI tools require written approval from [POLICY OWNER NAME AND TITLE] before use.
Approved tools and permitted tiers:
[APPROVED TOOLS, copy and customize this table]
| Tool | Approved plan | Permitted uses | Conditions |
|---|---|---|---|
| [Tool name] | [Business/Enterprise/API] | [Drafting, coding, summarizing, etc.] | [e.g., must be logged into company account] |
| [Tool name] | [Business/Enterprise/API] | [Specific use cases] | [Any conditions] |
Not approved without prior review:
- Personal or consumer-tier AI accounts (e.g., free ChatGPT, personal Claude.ai, personal GitHub Copilot) used for company work
- AI tools embedded in third-party SaaS products not on this list
- Browser extensions that send page content to AI services
If you are unsure whether a tool is approved, ask [POLICY OWNER NAME AND TITLE] before using it.
Section 2: Data Prohibitions
The following data must never be entered into any AI tool, including approved tools, unless a specific exception is granted in writing:
Absolute prohibitions:
- Passwords, API keys, credentials, tokens, or secrets, active or expired
- Customer personally identifiable information (PII): names, email addresses, phone numbers, account numbers, payment card data, or any other data that identifies a specific customer
- Employee personal data (beyond what is strictly necessary for an explicitly approved HR use case)
- Proprietary source code, algorithms, or technical specifications covered by an NDA with a client or partner
- Protected health information (PHI) as defined under HIPAA, unless a HIPAA Business Associate Agreement is in place with the AI vendor
- Any data classified as confidential or restricted under
[COMPANY NAME]'s data classification policy
Handle with care (minimize before inputting):
- Production configuration files, remove sensitive values before sharing with AI
- Customer support transcripts, remove names and account identifiers before sharing
- Financial projections containing deal-specific data, use anonymized or aggregated versions
- Internal legal communications
The test before sending: Before pasting any document or code into an AI tool, ask: "If this data were exposed in a breach, what would the consequence be?" If the answer is "significant," do not send it.
Section 3: Human Oversight Requirements
AI output requires human review before action in these contexts:
| Use case | Required review level | Reviewer |
|---|---|---|
| Customer-facing communications | Full review and approval | Sender |
| Legal or compliance documents | Review by qualified person before use | [Role] |
| Code merged to production | Standard code review, plus AI-specific security check | Reviewer/approver |
| Financial decisions or projections | Human verification of all numbers | [Role] |
| Hiring or performance decisions | Human decision with AI as input only | [Role] |
| Medical, legal, or safety advice | Not to be provided via AI without professional review | [Role] |
"AI suggested it" is not an excuse for errors in any of these categories. The employee who sends the communication, merges the code, or makes the decision is responsible for the output.
Section 4: Prohibited Uses
In addition to the data prohibitions above, the following uses of AI are prohibited regardless of tool or tier:
Always prohibited:
- Using AI to write fake reviews or testimonials, including reviews by people who don't exist or never used the product
- Using AI to generate or distribute content that discriminates against protected classes in employment, housing, credit, or public accommodation
- Using AI to deceive customers about whether they are interacting with a human or AI system, AI interactions must be disclosed
- Using AI to produce content that violates copyright in ways that create legal liability for
[COMPANY NAME] - Using AI to generate, analyze, or distribute content that is illegal in any jurisdiction where
[COMPANY NAME]operates
[INDUSTRY-SPECIFIC PROHIBITIONS], add uses prohibited in your context:
Examples for healthcare teams:
- Using AI to generate clinical recommendations that are provided to patients without physician review
- Processing patient PHI in any AI tool without a signed HIPAA BAA from that vendor
Examples for financial services teams:
- Using AI to generate credit scores, risk ratings, or investment recommendations without human review and adverse action notice procedures
- Processing data subject to FCRA in AI tools without appropriate data processing agreements
Examples for legal teams:
- Using AI output as the basis for legal advice to clients without attorney review and verification
- Processing privileged communications in third-party AI tools without client consent
Section 5: Privacy and AI Disclosure
Customer disclosure: If customers interact with an AI system at [COMPANY NAME], via chatbot, automated email, or AI-assisted support, they must be informed that AI is involved. A clear disclosure at the start of the interaction satisfies this requirement: "You are chatting with an AI assistant. [Optional: A human agent is available if you prefer.]"
Employee disclosure: Employees whose work is evaluated, monitored, or screened using AI tools must be informed. If [COMPANY NAME] uses AI in hiring, performance management, or access control, affected employees must receive notice.
Marketing claims: Any AI capability claim in marketing materials (accuracy rates, bias reduction, speed claims) must have documented evidence on file before publication. Repeating a vendor's claim makes it our claim; get the vendor's evidence first.
Section 6: Violation Reporting
If you accidentally send prohibited data to an AI tool:
- Stop immediately, close the session if possible
- Report to
[POLICY OWNER NAME AND TITLE]the same day - If the data included active credentials, rotate them immediately
- Document in the AI incident log: date, tool, what was sent, action taken
Deliberate violations of this policy, knowingly sending prohibited data, using unapproved tools for restricted purposes, or generating prohibited content, are subject to disciplinary action up to and including termination.
Reports are confidential. Retaliation against good-faith reporters is prohibited.
Section 7: Policy Updates
This policy is reviewed annually. When significant new AI tools are deployed or when regulatory requirements change, the policy is updated and all affected employees are notified.
The current approved tools list is maintained separately and updated as needed between full policy reviews.
[COMPANY NAME] | [EFFECTIVE DATE] | Owner: [POLICY OWNER NAME AND TITLE]
Why each section is there
The template isn't legal advice, but most sections answer a specific rule. Here's the mapping.
| Policy section | Rule it answers | What the rule says |
|---|---|---|
| 1. Approved tools, company accounts | GDPR Article 28(3) | "Processing by a processor shall be governed by a contract or other legal act" binding the processor; a consumer AI account usually comes with no such contract |
| 2. No PHI without a BAA | HIPAA, 45 CFR 164.502(e) | A covered entity may disclose PHI to a business associate only "if the covered entity obtains satisfactory assurance that the business associate will appropriately safeguard the information" |
| 4. No fake reviews | FTC rule, 16 CFR 465.2 | Writing or creating a review that misrepresents "That the reviewer or testimonialist exists" is an unfair or deceptive practice |
| 5. Customer disclosure | EU AI Act Article 50(1), from August 2, 2026 | Providers must design AI systems that interact with people so that people "are informed that they are interacting with an AI system" unless it's obvious |
| 5. Employee disclosure | EU AI Act Article 26(7) | Employers must inform workers' representatives and affected workers before using a high-risk AI system at the workplace; the high-risk rules apply from December 2, 2027 for Annex III uses |
| Briefing and training | EU AI Act Article 4 | Providers and deployers "shall take measures to support the development of AI literacy of their staff" |
Article 50(1) is a duty on the provider of the chatbot, not on you as the business using it. We keep the disclosure rule in the policy anyway, because it's cheap and customers expect it.
AI literacy: the briefing counts
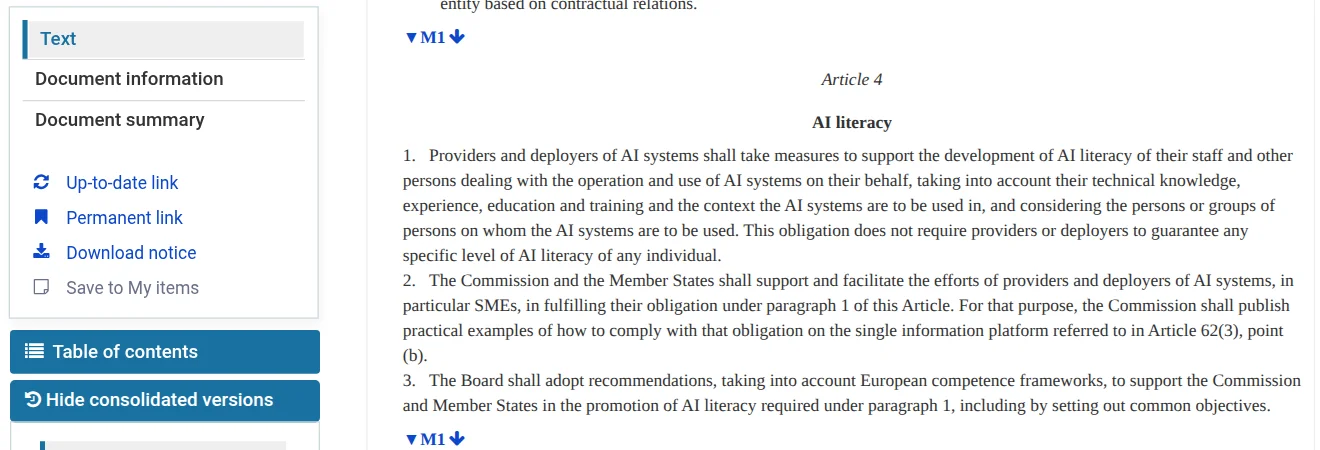
Screenshot: EUR-Lex, Regulation (EU) 2024/1689, consolidated text of July 27, 2026, Article 4. Captured October 31, 2026.
Article 4 has applied since February 2, 2025. The 2026 amendment softened it: providers and deployers must take measures to support AI literacy, and the text now says "This obligation does not require providers or deployers to guarantee any specific level of AI literacy of any individual." The Commission and member states are to support SMEs and publish practical examples.
For a small team, a 30-minute walkthrough of this policy, with a record of who attended, is a reasonable measure. Repeat it when you add a tool that touches customer data. The European Commission's AI Pact webinar on AI literacy goes deeper:
How to customize Section 1 (approved tools)

Photo: Unsplash, used under the Unsplash License.
The approved tools list is the part you'll change most. Three steps:
- Inventory what the team uses. Run a short survey and check expense reports for AI subscriptions. Include AI features inside tools you already pay for, such as note-taking, writing and CRM add-ons.
- Check the contract for each tool. If a vendor processes personal data for you, you need a data processing agreement. The AI vendor DPA tracker lists which vendors offer one and on which plans. No contract, no place on the approved list without a written exception.
- Set permitted uses per tool. A writing assistant used for internal drafts is a different risk from an AI feature inside your customer support system.
What admins say about rolling one out
On r/sysadmin, an admin at a HIPAA-covered company asked how others handle AI in regulated environments. u/Tall-Geologist-1452 replied: "It's also advisable to bring in legal and HR to help with the policy. After you get the policy completed, you need a way to enforce it." u/OkEmployment4437 added: "In regulated environments I'd also require written sign-off from compliance/data owners for each approved use case, not just a blanket "AI is allowed.""
Both points fit the template. The approved tools table in Section 1 is where the per-use-case sign-off goes, and blocking unapproved AI domains on company devices is the enforcement that keeps Section 1 true.
After you deploy the policy
- Brief the team. Cover the data prohibitions and the human review table first; they're the two sections we'd prioritize. Keep the attendance record.
- Start an AI incident log. A spreadsheet with date, tool, what happened and action taken. It's the record you'll want if a client, auditor or regulator asks how you govern AI.
- Set a review date. Review the policy at least once a year, and update the tools list whenever you approve or drop a tool.
How to tell if it's working
The policy works if staff can answer three questions without looking: which tools are approved for their role, what data never goes into any AI tool, and who to contact when something goes wrong. Ask three people at random. If the answers differ, run the briefing again and shorten the data rules. Three prohibitions people remember beat twelve they don't.
Our take
In our view, an AI policy does more good short than complete. This one is meant to be short and enforceable: a tools list, a data list, a review table and a reporting path. The legal mapping above shows that each section answers something real, but the policy only helps if the tools list matches what staff use, so start there and update it every time someone asks for a new tool.
Correction (October 31, 2026): An earlier version said the template was "structured to satisfy FTC requirements for substantiated AI use claims and EU AI Act transparency obligations for Limited-Risk and High-Risk deployers," cited EU AI Act Article 13 as "transparency obligations for deployers" and Article 28 as "deployer obligations," and said most small teams don't need legal review. Article 13 covers information providers give deployers of high-risk systems, Article 28 concerns notifying authorities, and deployer obligations are in Article 26. No template satisfies those laws on its own; the references now point to the specific rules each section answers.
Related reading
- AI acceptable use policy, detailed implementation guide
- AI vendor DPA tracker 2026
- AI tool register template
- AI governance guide for small teams
- AI agent governance for small teams: policy template and audit log
- ChatGPT usage policy for employees: 3-tier rules template
- AI governance for remote and distributed teams