Image: Pexels, used under the Pexels License.
You need this if anyone on your team connected their own OpenAI, Anthropic or Google key to an OpenCode Console workspace. Those keys may now be in someone else's hands, and the fix doesn't happen in OpenCode. It happens in each provider's dashboard, and the checklist below runs in the order that limits the bill.
Event date: the night of October 16, 2026 (breach, per OpenCode). First reports: October 17, 2026: OpenCode's own post on X, then Startup Fortune and OfficeChai within the hour.
What OpenCode has said
OpenCode posted on October 17 that it "had a security breach last night related to a large scale distillation attack," that it had emailed every affected user that morning, and that "If you did not get an email you were not impacted." The affected group was "a subset of users who had external providers linked." According to Dealroom, the email blamed "unauthorized access to a legacy system that we were in the process of decommissioning." Co-founder Dax Raad added on X that this was "the OpenCode Console, not OpenCode itself," and that keys used in the local app "never come to us."
https://x.com/opencode/status/2111519637049319818
Users had already found charges. Colin Parsons wrote that his OpenAI key was "pounded" for $281 and his Anthropic key for $168, Dealroom reported, and Preston Zeller put his losses at $1,700. Anthropic said it revoked affected Claude API keys, per the same report.
Who needs this checklist
- Anyone with a provider key saved in a Console workspace. Console's Providers API page says "Console adds the provider credential before forwarding," which means OpenCode holds the key, not your machine.
- Teams where one person set up Console for everyone. OpenCode notified affected users by email. If you can't confirm that everyone who might have saved a key got it, run the checklist anyway.
- Not, by OpenCode's account, people who only use the CLI or desktop app with their own keys. Rotating those costs little if you're unsure.
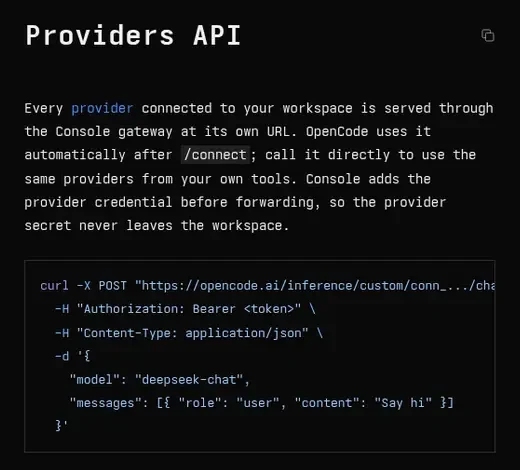
Screenshot: OpenCode Console Providers API documentation, OpenCode. Captured October 19, 2026.
The checklist
Copy this into your incident ticket and tick it off per key.
| # | Step | Where | Done when |
|---|---|---|---|
| 1 | Revoke every key that was saved in Console | OpenAI API keys page; Anthropic Console, API keys, "Delete API Key"; Google Cloud credentials | The old key no longer appears as active |
| 2 | Create a new key and store it in a secrets manager | Same pages | New key exists, isn't in any repo or chat |
| 3 | Update every app, script and CI job that used the old key | Your code and CI secrets | Nothing breaks on a test run |
| 4 | Pull usage and billing for each provider, back to October 16 at least | Provider usage and billing pages | You've saved a copy of anything you didn't run |
| 5 | Report unexpected usage to the provider's support | OpenAI Help Center chat; Anthropic support | Ticket number recorded |
| 6 | Set a hard spend limit and alerts at the provider | OpenAI project or org limits; Google API key restrictions | Limits saved |
| 7 | Give each tool and teammate its own key | Provider dashboards | One key per tool, named |
| 8 | Revoke and reissue Console service-account keys | Console, Keys, service account, API Keys | Old Console keys return 401 |
| 9 | Ask OpenCode in writing what was exposed and when access began | Your vendor contact | Written answer filed |
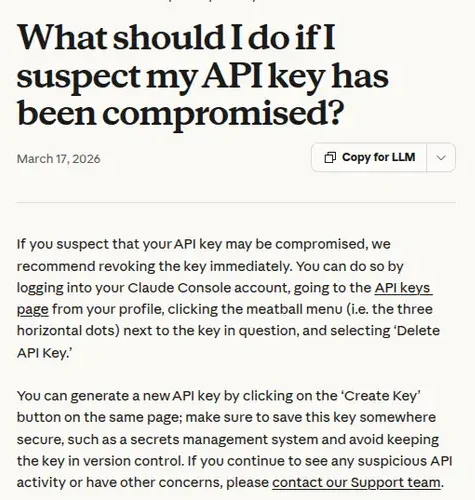
Screenshot: "What should I do if I suspect my API key has been compromised?", Anthropic Help Center. Captured October 19, 2026.
How to fill it in
Steps 1 and 2 come from the providers themselves. Anthropic's help article says "we recommend revoking the key immediately" and to save the new one "somewhere secure, such as a secrets management system." OpenAI's account security page says to delete the key, "Review your API usage for unexpected activity and keep the details," then contact support.
Step 4's date is a floor, not a fact. OpenCode dated the breach to the night before its October 17 post but hasn't said when the access began, so if your usage looks odd earlier, go back further.
Step 6 has to happen at the provider. OpenCode's budgets page caps spend that flows through Console, and "Without any budget, spend is unlimited." A copied key used directly against OpenAI or Anthropic never touches Console, so only the provider can stop it. OpenAI notes its hard limit enforcement "is not instantaneous," so set alerts below the limit too. Google's API key guidance adds restrictions, which limit "the impact of a compromised API key."
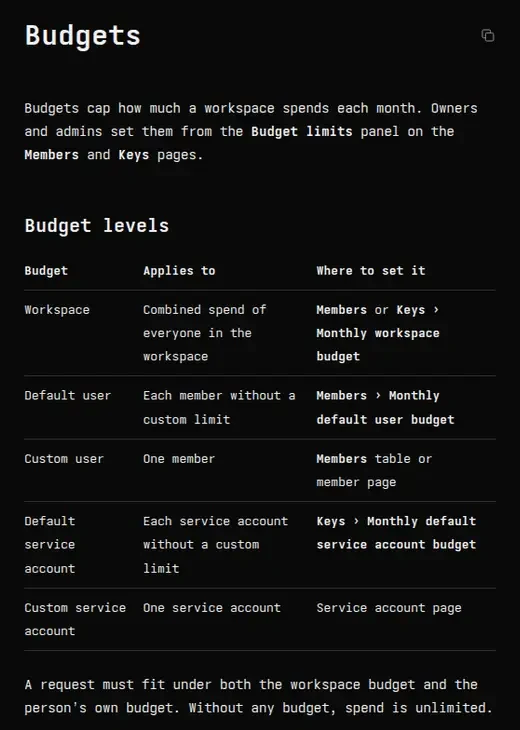
Screenshot: OpenCode Console Budgets documentation, OpenCode. Captured October 19, 2026.
Step 8 is a precaution. OpenCode hasn't said Console's own service-account keys were touched. Its docs say "Removing the service account revokes all its keys," and reissuing them takes a few minutes.
Step 9 is your vendor file. Ask what the legacy system was, how many keys it held, whether keys were encrypted at rest, and when access began. We found no public answer to any of those as of October 19. Our AI vendor contract redline template has breach-notice clauses you can add when the contract comes up for renewal.
What it doesn't cover
It won't tell you whether a provider will refund usage you didn't run; that's between you and their support team, which is why step 4's saved evidence matters. It doesn't cover the distillation claim either: OpenCode hasn't named anyone or explained how the breach and the distillation attack connect. And if a key belonged to a client's account, the bill is theirs: tell them today.
What Console users are saying
On r/opencode, the most-upvoted replies questioned the explanation. "The distillation attack was the effect, not the cause," wrote u/fastvroomy, adding that "the only path in situations like this is complete transparency." One affected user, u/pas-un-robot, wrote: "I was affected and a few of the attackers chats were saved in my chat logs," then added, "not that it proves anything."
Related Reading
- LiteLLM supply chain attack: what to check and rotate
- Claude Token Theft via Infostealer: 5 Enterprise Controls
- AI Vendor Supply Chain Security: Checklist for Small Teams
- OpenAI agents and the RubyGems attack: what's confirmed
- AI Vendor Contract Redline Template: 12 Clauses to Add or Fix
- AI Vendor Security Incident Response: A 4-Step Playbook
- AI Agent API Token Leak: 24-Hour Incident Response Playbook