Image: Pexels, used under the Pexels License.
Use this if someone has told you Texas gives a safe harbor to companies that adopt the NIST AI Risk Management Framework. It doesn't, at least not in those words. The Texas Responsible Artificial Intelligence Governance Act (HB 149, in force since January 1, 2026) protects a company that finds its own violation through an internal review built on a recognized framework. The framework it names is NIST's Generative AI Profile, not AI RMF 1.0 on its own (enrolled text).
That's a narrower promise, and a more useful one. It rewards a review that runs and produces findings, which is what the steps below build.
What Section 552.105(e) says
The clause, in full:
(e) A defendant in an action under this section may not be found liable if: (1) another person uses the artificial intelligence system affiliated with the defendant in a manner prohibited by this chapter; or (2) the defendant discovers a violation of this chapter through: (A) feedback from a developer, deployer, or other person who believes a violation has occurred; (B) testing, including adversarial testing or red-team testing; (C) following guidelines set by applicable state agencies; or (D) if the defendant substantially complies with the most recent version of the "Artificial Intelligence Risk Management Framework: Generative Artificial Intelligence Profile" published by the National Institute of Standards and Technology or another nationally or internationally recognized risk management framework for artificial intelligence systems, an internal review process.
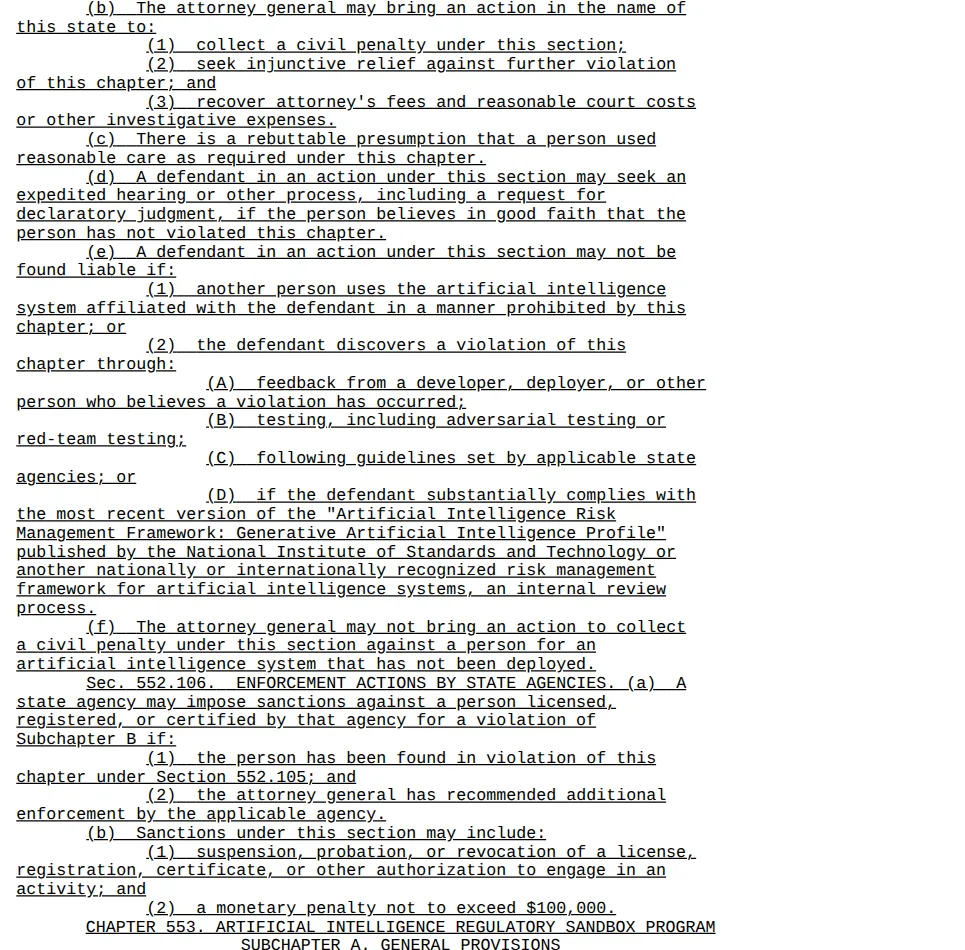
Screenshot: HB 149 enrolled text, Section 552.105, Texas Legislature Online.
| Route | Who triggers it | What to keep |
|---|---|---|
| (e)(1) Someone else misused your system | A customer or user | Terms of use, the misuse report, what you did about it |
| (e)(2)(A) Feedback | A developer, deployer or anyone who reports a suspected violation | A reporting channel and its log |
| (e)(2)(B) Testing | You, including adversarial or red-team testing | Test plans, results, fixes |
| (e)(2)(C) State agency guidelines | You, following them | Which guidelines, and when you applied them |
| (e)(2)(D) Internal review | You, while substantially complying with the NIST Generative AI Profile or another recognized framework | The framework mapping, the review calendar, findings and changes |
Three other provisions sit next to it. The law presumes you used reasonable care, and the Attorney General can rebut that (Sec. 552.105(c)). You can ask for an expedited hearing or a declaratory judgment if you believe in good faith you didn't violate the law (Sec. 552.105(d)). And before any lawsuit, the Attorney General has to give written notice and a 60-day cure window (Sec. 552.104).
What the defense doesn't do
- It doesn't stop an investigation. After a complaint through the Attorney General's online mechanism, the office can issue a civil investigative demand for a description of each system's purpose, training data, inputs, outputs, metrics, limitations and monitoring (Sec. 552.103). The defense matters in a lawsuit, later.
- It isn't about AI RMF 1.0 alone. The text names the "most recent version" of the Generative AI Profile. That's NIST AI 600-1, published July 26, 2024 as a companion resource to AI RMF 1.0. NIST released AI RMF 1.0 on January 26, 2023 and says it's being revised under the White House AI Action Plan (NIST), so check for a newer profile at every review.
- No one approves your framework. The law doesn't give the Attorney General a list of approved frameworks, and it doesn't define "substantially complies."
- It doesn't cover everything at once. It's a defense to liability for the violation you discovered. The bans themselves still apply.
The misreading travels. A February 2026 r/grc post by u/Top-Refrigerator2918 said "TRAIGA Section 546.103 recognizes demonstrable NIST AI RMF compliance as an affirmative defense against $200K/violation enforcement by the Texas AG." HB 149 has no Section 546.103, and the defense it does have is the one quoted above. Law firm summaries split too: Baker Botts lists "Substantially comply with the NIST AI Risk Management Framework or other recognized standards" as its own defense, while Norton Rose Fulbright ties it to discovery: "If a company discovers a potential violation in one of these ways, they cannot be found liable." We read the text the second way, because route (D) sits in the list of ways a defendant "discovers a violation."
https://www.reddit.com/r/grc/comments/1r2z35j/nist_ai_rmf_now_has_statutory_teeth_in_texas/
Steps: build the review the defense rewards
Screenshot: NIST AI 600-1 publication page, National Institute of Standards and Technology.
- Name the framework in writing. Pick NIST AI 600-1, used with AI RMF 1.0, or another recognized framework. ISO/IEC 42001 is a strong candidate, though the text doesn't name it. Record the version and the date you adopted it.
- List the systems in scope. Anything you develop or deploy in Texas, or that Texans use (Sec. 551.002). One row per system, with an owner.
- Screen each system against the bans. Manipulation toward self-harm, harm or crime; unlawful discrimination; constitutional rights; sexual deepfakes and child sexual abuse material (Secs. 552.052-552.057). Health care providers add the patient disclosure (Sec. 552.051(f)). Our TRAIGA compliance checklist has the section-by-section table.
- Test, including adversarial testing. Red-team prompts for self-harm and minor impersonation on chat products. Route (B) counts on its own, so keep the results whether or not the review finds anything.
- Open a reporting channel. A form or inbox where a developer, deployer, customer or employee can report a suspected violation. Route (A) depends on it, and every report gets a date and a response.
- Run the review on a schedule and log what it finds. Date, system, which route surfaced the problem, what you changed. A review that never finds anything isn't evidence of much; a findings log with fixes is.
- Prepare the cure. If notice arrives, you have 60 days to cure and send a written statement saying you cured the violation, with supporting documentation and the internal policy changes that prevent a repeat (Sec. 552.104(b)(2)). Draft the template now.
What to keep

Image: Unsplash.
| Record | Why it matters |
|---|---|
| Framework decision (name, version, date) | Shows which framework your review "substantially complies" with |
| System inventory with owners | Defines the review's scope |
| Review calendar and minutes | Shows the review actually runs |
| Findings log (date, route, fix) | The discovery the defense turns on |
| Test plans and results | Route (B) evidence |
| Reporting channel log | Route (A) evidence |
| Investigative demand answer pack | The descriptions Section 552.103(b) lists, per system |
| Cure statement template | The three items Section 552.104(b)(2) requires |
Penalties, for scale: an uncured violation the court calls uncurable runs $80,000 to $200,000 each, and a curable one $10,000 to $12,000 (Sec. 552.105(a)). The Attorney General enforces alone, with no private right of action (Sec. 552.101).
What we could not confirm: we found no Attorney General guidance on what "substantially complies" means, no court decision applying Section 552.105(e), and no public TRAIGA enforcement action. The office's Consumer AI Rights page, checked October 20, 2026, lists the bans and penalties and doesn't mention the defense.
Related resources
For the documents behind steps 2 and 6, start from an AI acceptable use policy template and an AI tool register template. For other state laws, see the AI regulation deadline calendar 2026. Colorado SB 26-189 has no framework safe harbor: its duties are notices, an adverse-outcome explanation, data correction, human review and records, which a NIST program doesn't produce by itself. Connecticut SB 5 doesn't reference a framework; for hiring tools it sets notice duties from October 1, 2027.
Correction (October 16, 2026): Earlier versions said Colorado SB 189 has requirements a NIST AI RMF program substantially addresses and described Colorado's law as imposing impact-assessment duties. Those duties belonged to the 2024 law, which never took effect; SB 26-189 has no safe harbor or impact assessment (signed act).
Correction (October 20, 2026): We rewrote this page after checking it against the enrolled text of HB 149. Earlier versions said substantial compliance with the NIST AI RMF is an affirmative defense, "a complete defense," that protects you "before a violation is ever alleged." Section 552.105(e) names NIST's Generative AI Profile or another recognized framework, and only as part of an internal review through which the defendant discovers a violation. They also described the AI system definition wrongly, listed exclusions (personal use, a HIPAA carve-out) the statute doesn't contain, said the cure must satisfy the Attorney General (the statute lists what the written statement must contain), cited "the AG's public guidance" that we couldn't find, and estimated per-violation totals "in the tens of millions" with no source. Those passages were removed.
Related Reading
- Texas TRAIGA compliance checklist 2026
- Texas TRAIGA Complaint Portal Is Live: What Changes for AI Teams Now
- ISO 42001 vs NIST AI RMF for small teams
- Multi-state AI compliance strategy 2026
- NYC Local Law 144: AI bias audit employer guide 2026
- AI regulation deadline calendar 2026
- AI acceptable use policy template
- AI tool register template
- Texas TRAIGA biometric AI hiring compliance 2026
- Great American AI Act 2026: which state AI laws survive federal preemption
- FCRA AI hiring disclosure requirements 2026
- Utah AI Policy Act compliance 2026
- ISO 42001 vs EU AI Act vs NIST AI RMF: which framework applies
- AI governance guide for small teams
- AI risk register template: a dated record of risks found and fixed